Enterprise security engineering
Five-plus years in regulated financial-services environments, owning practical network, identity, and security controls.
Security engineering · Vulnerability research · Offensive security · Automation
Security engineering, vulnerability research, and practical offensive testing.
I work across enterprise networks, identity, applications, cloud infrastructure, and security automation—finding weaknesses, validating meaningful risk, and translating findings into remediation that works in production.
What I help teams decide
Proof points
Five-plus years in regulated financial-services environments, owning practical network, identity, and security controls.
Assess exploitability, emulate threats, validate controls, and turn evidence into remediation teams can execute.
Build custom Python, PowerShell, Bash, and API-driven tools for repeatable testing and evidence collection.
Decision process
Connect enterprise security engineering, vulnerability research, and offensive validation to actions teams can execute.
Keep source links, assumptions, and reviewer state visible so security decisions can be checked quickly and communicated clearly.
Best for vulnerability triage, cloud/release review, and product-security advisory work when teams need a sharper decision path instead of more alerts.
Supporting proof
Recognition
Supporting signal from the same reporting trail.
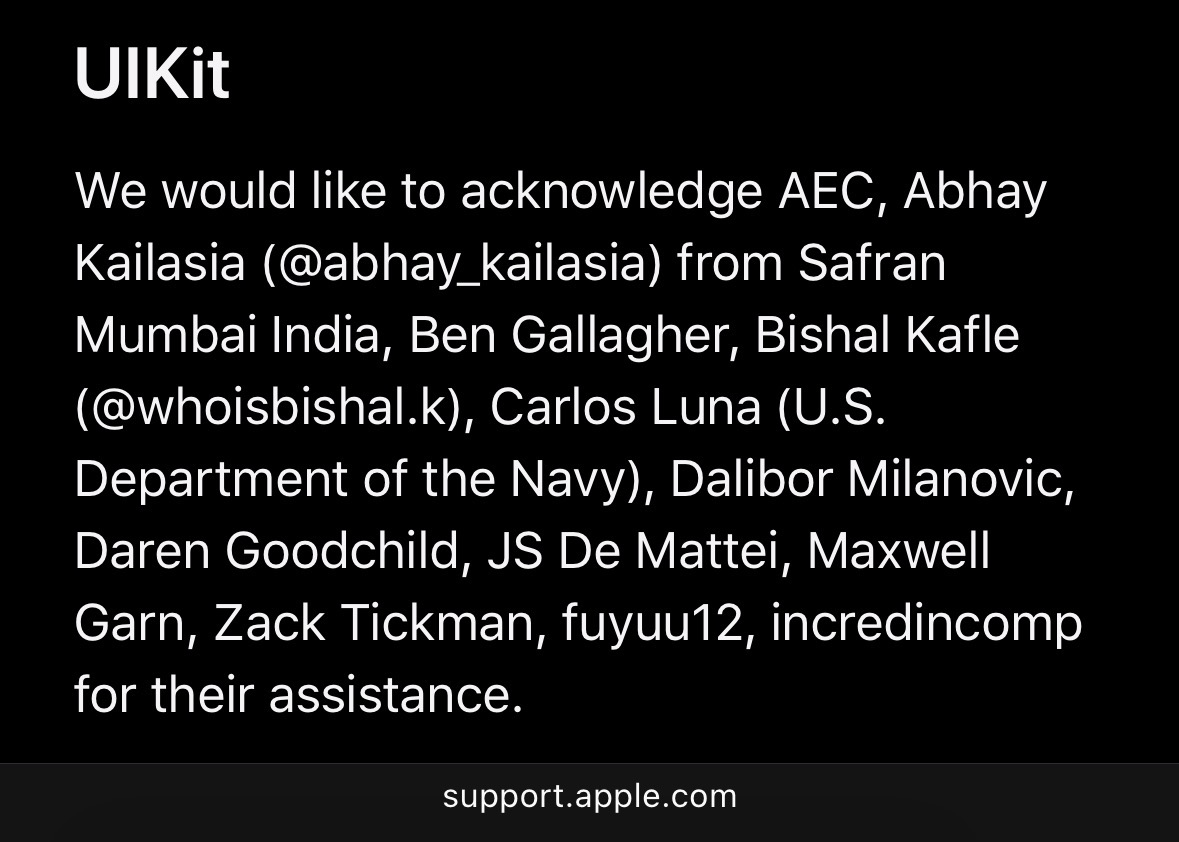
Apple publicly credits incredincomp in five security advisories covering iOS/iPadOS, macOS, tvOS, watchOS, and visionOS. This is independent recognition, not employment or a CVE assignment.
Responsible vulnerability reporting with safe reproduction, exploitability analysis, evidence, and useful remediation detail.
Independent work
Supporting signals that show practical tooling and public security-education reach.
Developer tooling
Created and launched a Visual Studio Code extension that adds file modification dates and context directly to the VS Code Explorer.
VS Code Marketplace · 2.0k+ installs
View on VS Code MarketplaceCommunity signal
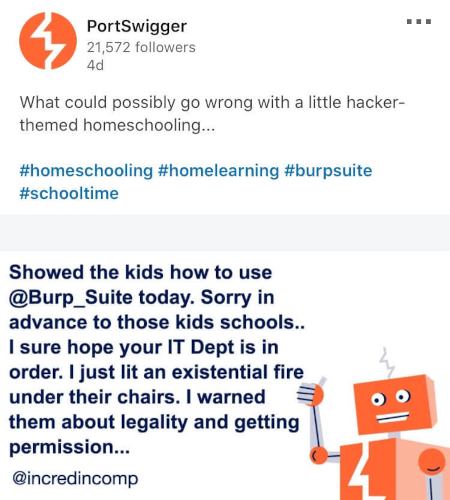
A public @incredincomp post about teaching Burp Suite was featured by PortSwigger in a LinkedIn update about security education.
Next steps
Bring vulnerability triage questions, cloud and release review decisions, product-security or advisory findings, or AI-assisted security operations queues. You get source-linked reasoning, clear assumptions, and practical remediation paths.
Public identity
Consulting